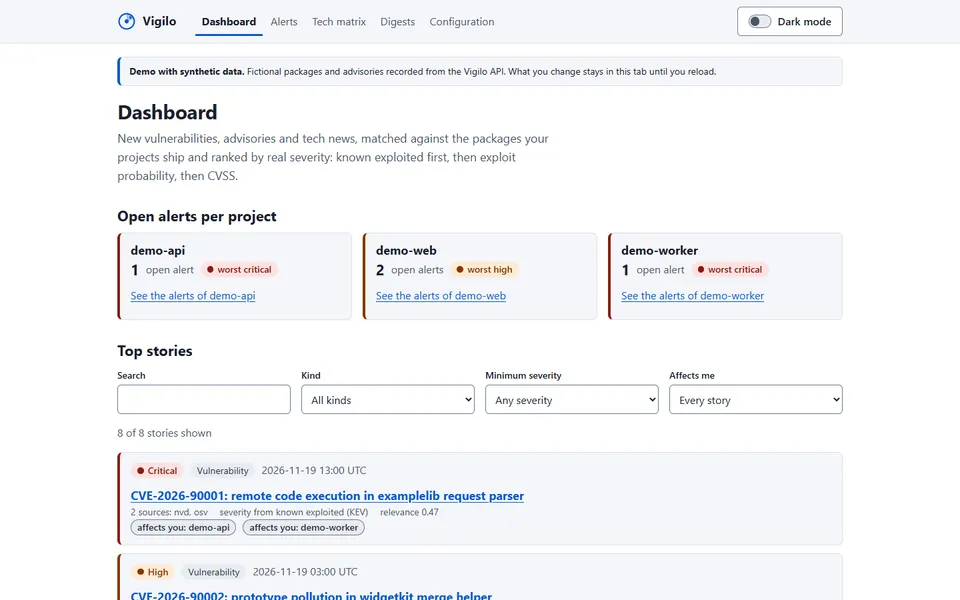
 Coming soon
Vigilo
Know what broke, why it matters, and whether it's yours
Developer tool
Vigilo
Know what broke, why it matters, and whether it's yours
The code lives in a private repository; this sheet and the demo, when there is one, show the work.
Draft. Written from the program notes and pending the author’s review.
- Status
- Coming soon
- Type
- Developer tool
- Running since
- February 2026
- Role
- Sole engineer
- Domains
- security, supply chain
- Cast
- Go, SBOM, OSV, GitHub Actions
Context and problem
A vulnerability researcher that matches OSV-Scanner with 1.0 precision and recall on its reference set.
Vulnerability feeds list thousands of advisories; teams cannot tell which ones reach code they actually ship (assumption documented in the repository).
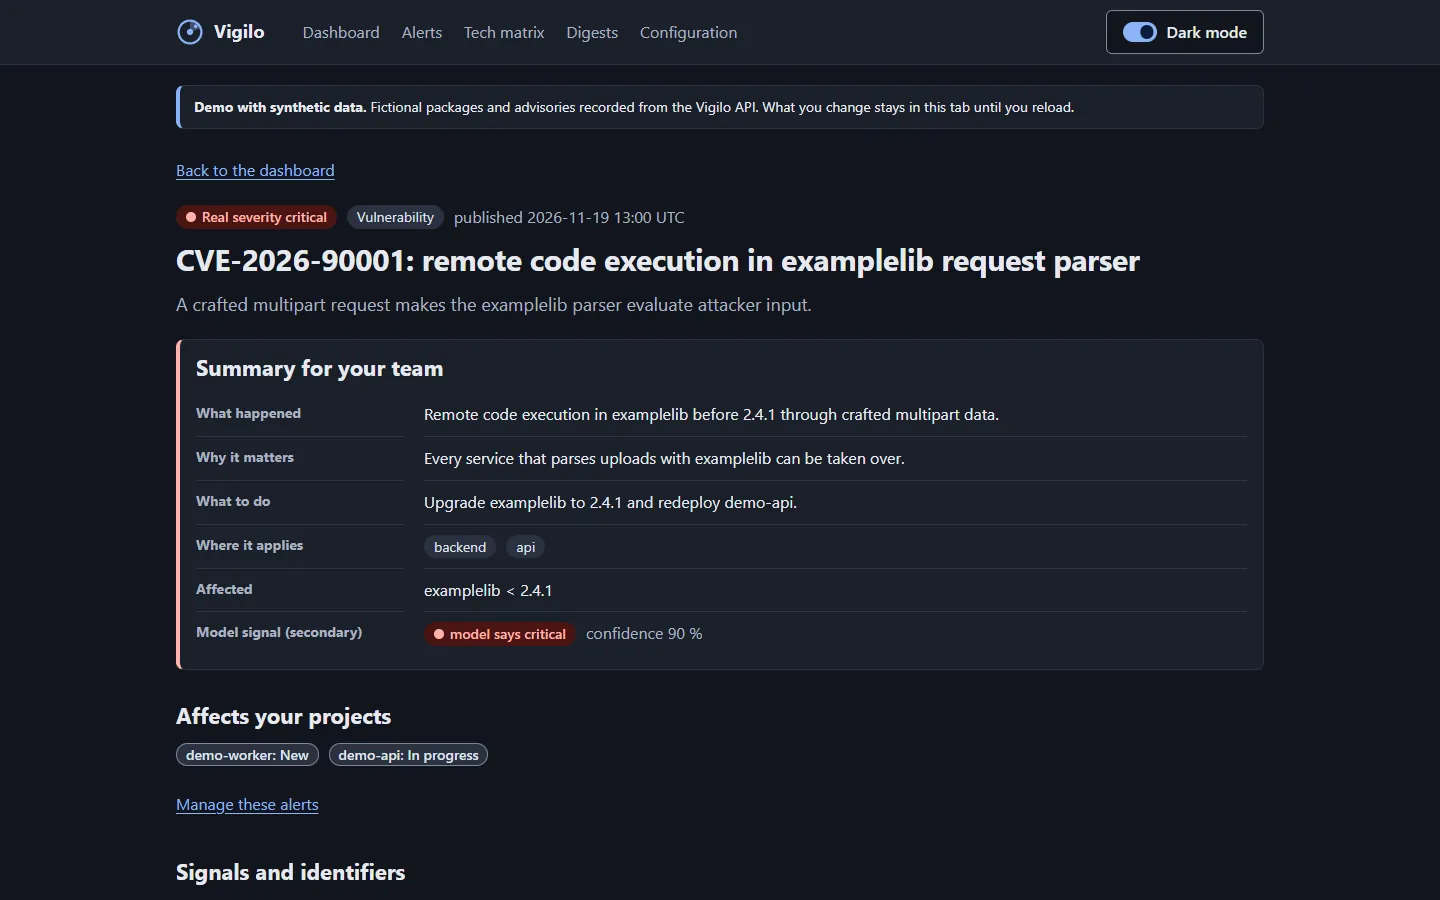
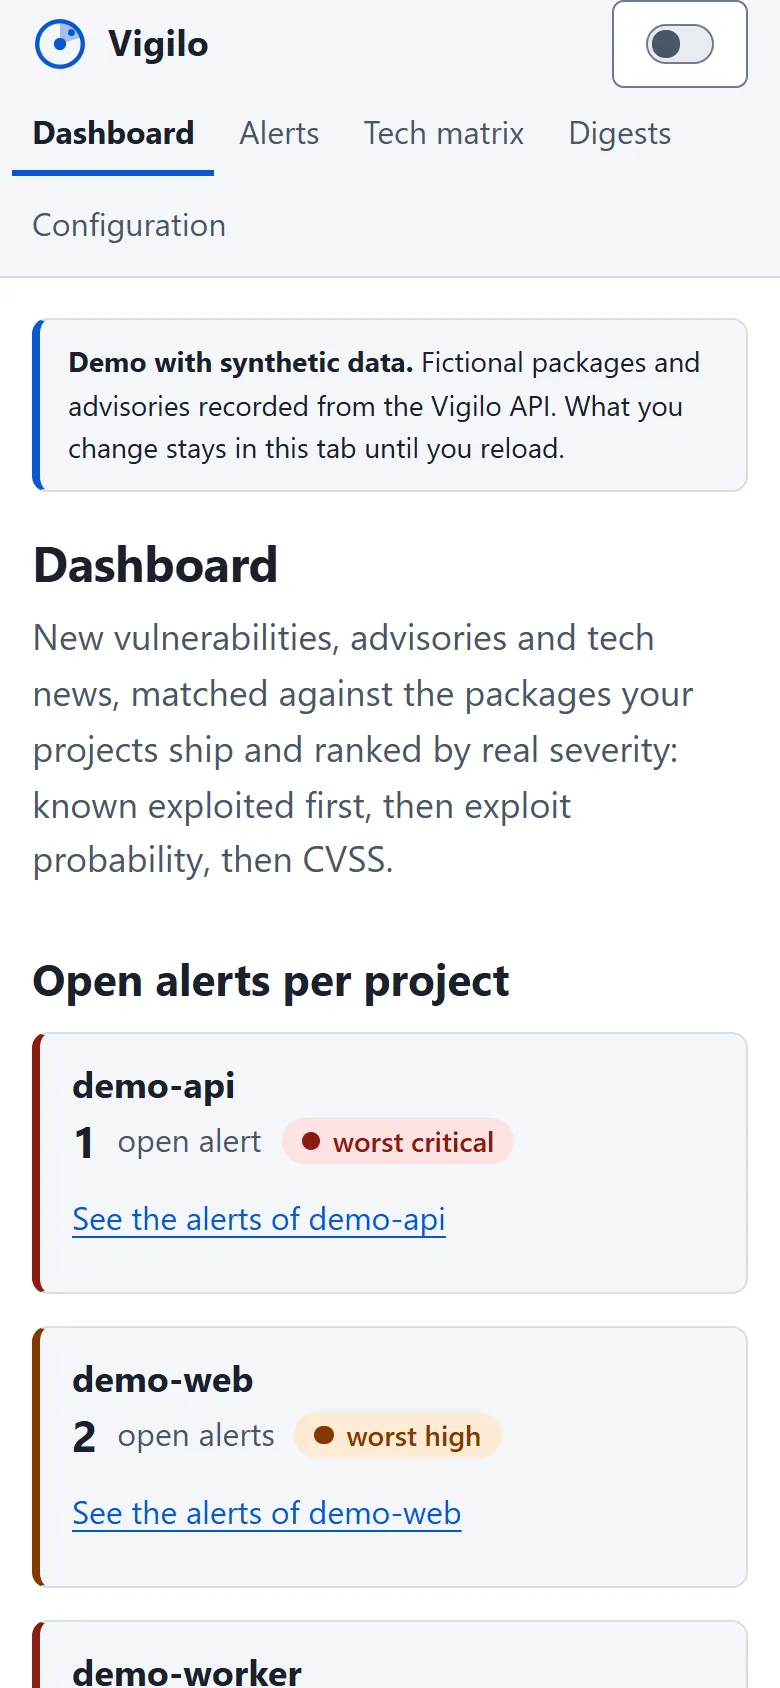
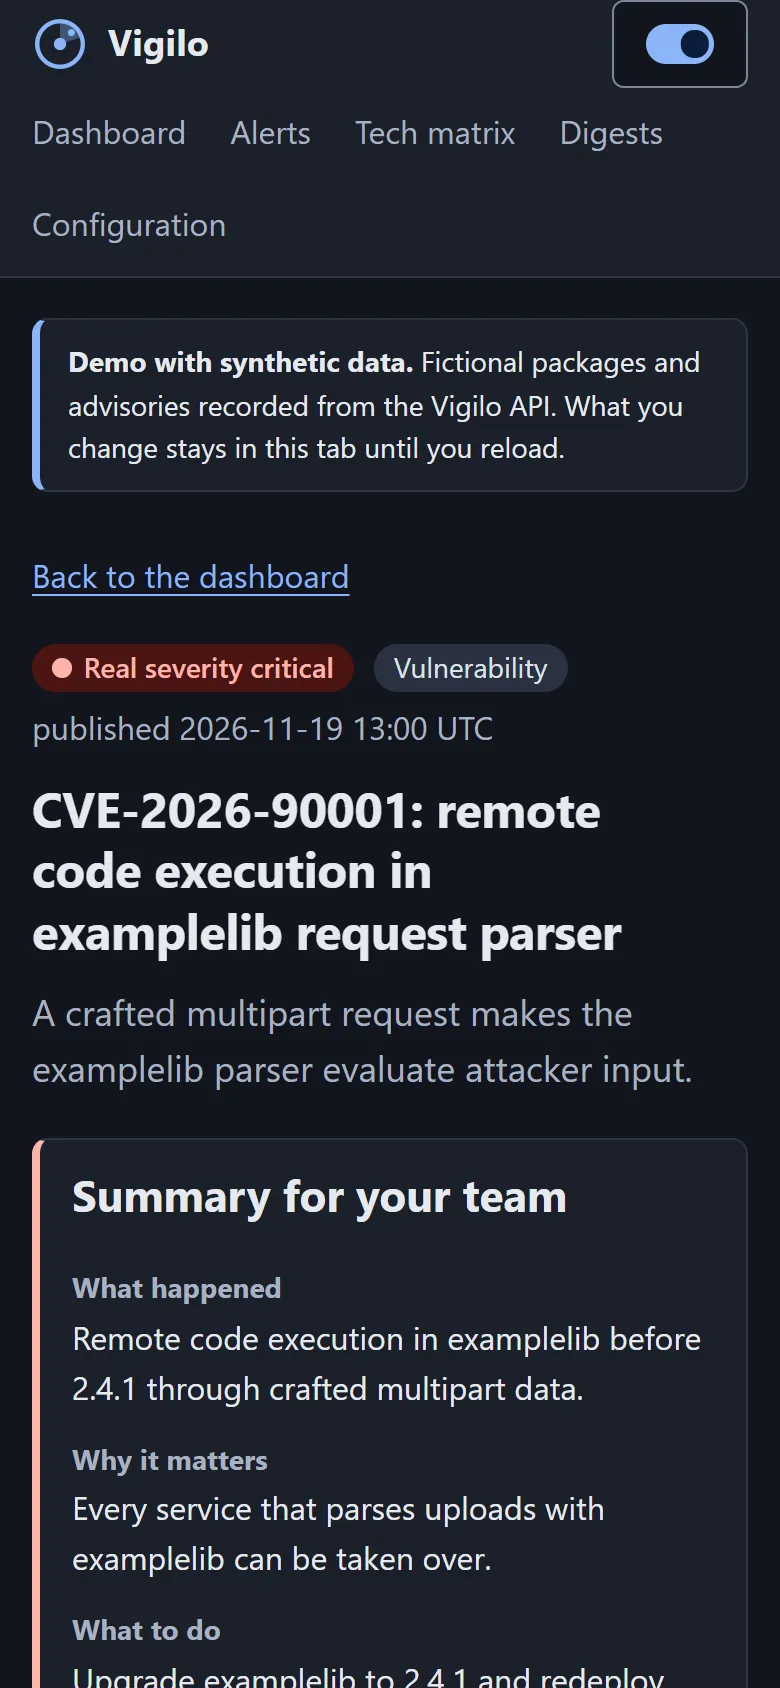
Screens
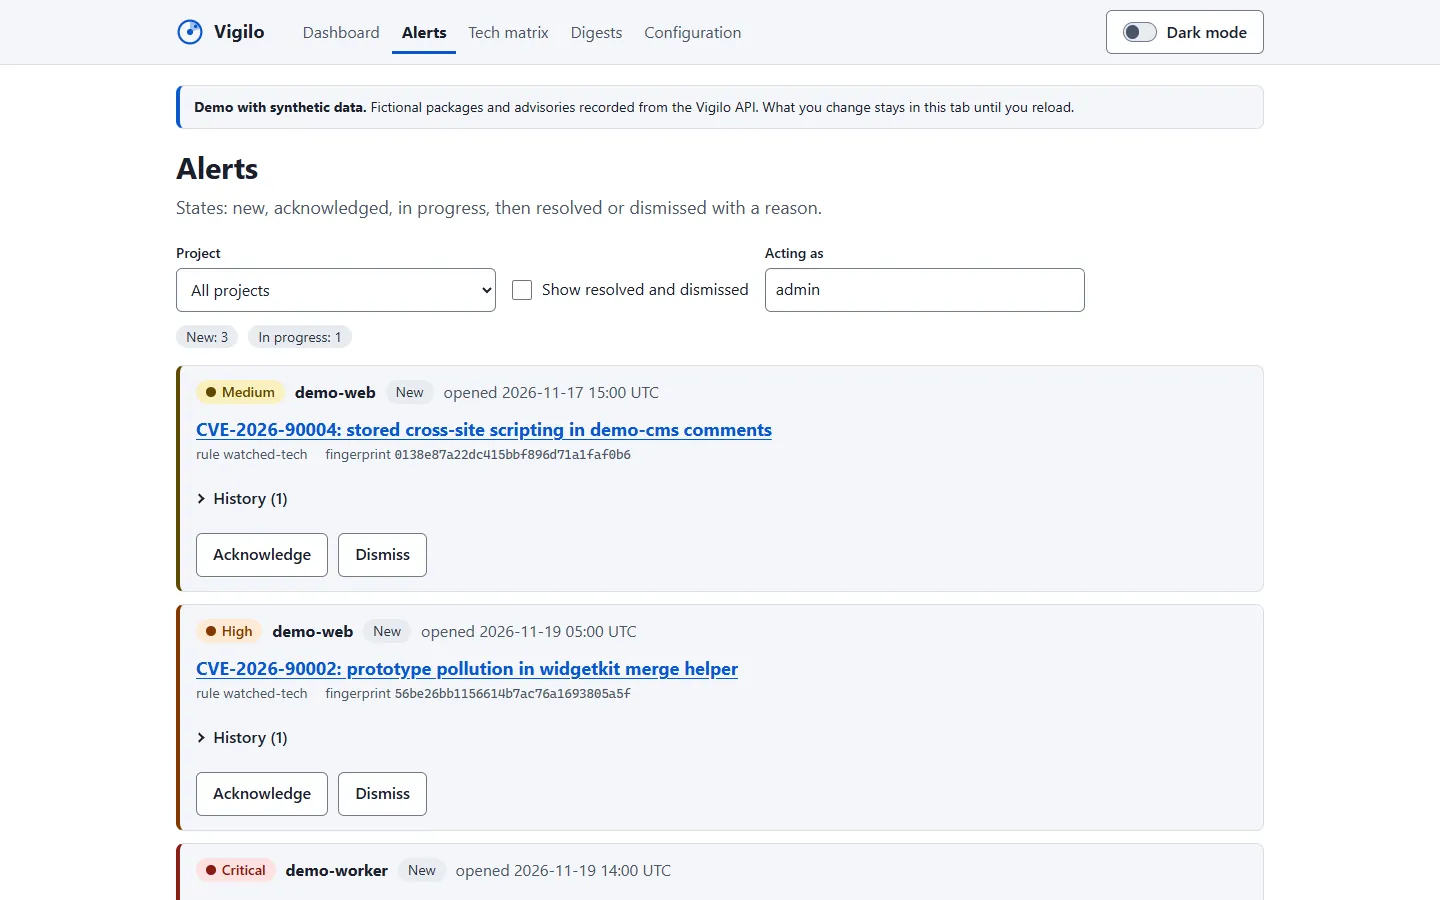
How it was built
Built in 13.3 h · USD 149.75 of AI · 1,350 tests · 5 audits
Source: Trysac/12b-vigilo-lite-investigador docs/development-report.md (lines 10, 13, 29), dated 21 November 2026.
Architecture and interfaces
- Provides
- cli vigilo, events vuln.*, api vigilo-api, file sbom.cdx.json
- Shared keys
- package_ref, endpoint
Results with dated evidence
Outcomes as stated in the manifest; the measured figures are the ones with a date.
- Advisories matched to the SBOM of each release, with reachability noted
Case study in preparation
The full case study adds these sections when it is published:
- Constraints
- Architecture diagrams (C4 context and containers)
- Three key decisions
- What went wrong
- Demo video
- What I would do differently
In the project mesh
Highlights
sbom, osv, supply chain